Showing posts with label SECURITY. Show all posts

Sunday, April 21, 2013

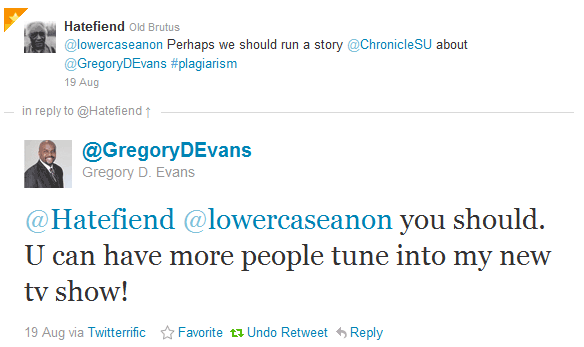
Joseph K Black plagiarizes Gregory D Evans | The Internet Chronicle

Joseph K Black plagiarizes Gregory D Evans

Famous for books that are 99.3% plagiarized, security charlatan Gregory D Evans has, for once, had his work stolen out from under him. Joseph K Black has adopted Gregory D Evans’ methods. Black has cited his doubtful “expertise” as a reason for people to pay attention to him. Joseph K Black is unapologetic about his obvious intellectual theft from Gregory D Evans, just as Evans embraces his place as a plagiarist.

twittershot Joseph K Black plagiarizes Gregory D Evans

Twitterrific is a Mac-only Twitter client, final proof of Gregory D Evans' fraudulent computer expertise.

Gregory D Evans obviously doesn’t care that he’s a plagiarist, as long as he gets his attention. He’s made many contradictory and uninformed comments for reporters who think he’s an expert on Anonymous or computer security.

This is a challenge to Joseph K Black: Step up your game if you want to outdo Gregory D Evans.

We tested this page and blocked content that comes from potentially dangerous or suspicious sites. Allow this content only if you’re sure it comes from safe sites.

Wednesday, March 20, 2013

Hacker Crackdown: Blame AT&T's Crappy Security,

Hacker Crackdown: Blame AT&T's Crappy Security, Not Weev

Another hacker bites the dust. This morning, Andrew Auernheimer — aka "Weev" — got handed a sentence of 41 months in prison, 3 years of supervised release and a $36,500 fine. All for basically exposing a major security hole at AT&T and publicly shaming the company that hadn't ever bothered to fix it.

Back in 2010, Auernheimer and his partner Daniel Spitler, part of a team calling itself Goatse Security, hacked into a public server owned by AT&T. That server housed hundreds of thousands of email addresses of customers who owned 3G iPads. Through trial and error and some ingenuity, group members discovered they could randomly guess iPad identification numbers and then use them to extract matching email addresses from that server.

AT&T's Security Loophole, Exposed

This security loophole on AT&T's site returned email addresses associated with ICC IDs, the unique serial numbers used to track and link SIM cards on mobile devices with specific subscribers. A PHP script that automated the process ended up harvesting a whopping 114,000 email addresses. Auernheimer then sent news of the group's work as an exclusive to Gawker.

(See also: U.S. Announces 120,000 iPad Users Had Their Data Stolen)

A day later in a blog post on the Goatse Security site, Auernheimer and company wrote:

I want to summarize this explicitly:

  • All data was gathered from a public webserver with no password, accessible by anyone on the Internet. There was no breach, intrusion, or penetration.
  • The dataset was not disclosed until we verified the problem was fixed by the vendor.
  • The only person to receive the dataset was Gawker journalist Ryan Tate who responsibly redacted it.

[...]

We did this to help you.

By its own account, AT&T responded with "swift action" to prevent additional intrusions: 

Within hours, AT&T disabled the mechanism that automatically populated the email address. Now, the authentication page log-in screen requires the user to enter both their email address and their password.

Problem solved, right? Wrong. A week later Auernheimer was arrested after the FBI raided his house. He was then charged with major computer crimes under the Computer Fraud and Abuse Act (CFAA), the same legal club prosecutors have used to go after Aaron Swartz and, last week, Reuters social editor Matthew Keys.

(See also: Reuters Social Editor Indicted Over Anonymous Hack; Internet's Jaw Drops)

During the trial, AT&T admitted the server was publicly accessible, yet claimed Auernheimer's access was unauthorized. Under the CFAA, unauthorized access is a crime. But the statute's ambiguity on that score has opened the door for egregious prosecutorial overreach in this and other cases.

On Nov. 20, 2012, a jury found Auernheimer guilty of one count each of identity theft and conspiracy to violate the CFAA. Today, Auernheimer was sentenced.

Fair Or Fanning The Flames?

Supporters of Auernheimer say what he did was not a crime. Maybe it wasn't smart to expose a major vulnerability at AT&T and then rub the company's nose, but stupidity shouldn't be a federal offense. Friends and colleagues point out that the point of hacking is to gain something from it — and in this case, there was no money involved and nothing else to gain but besides a measure of celebrity.

Australian journalist and hacktivist Asher Wolf wrote a poignant piece today arguing that's it's insane to publicly tar and feather someone who spurred a company to fix a problem, even if he didn't choose the most orthodox means of doing it:

Putting Weev behind bars is pointless and tragic. Jailing the most outspoken men and women amongst our generation won’t stop the leaks, the hacks, the news revelations, the whistleblowers — and most of all it won’t stop the rage of the malcontent, dispossessed youth from eventually tumbling down upon the heads of the bureaucrats who sold us out and then tried to lock us up when we complained.

Bees To Honey

AT&T's vulnerability was basically low hanging fruit — just too easy a target for hackers to ignore. But the question of whether AT&T was asking for it is more complicated.

Sure, poor security is asking for trouble. But playing with fire will get you burned no matter how righteous and ethical you claim to be. "Our conduct doesn't happen in a vacuum," hacker Adrian Lamo — the guy who allegedly dropped a dime on Bradley Manning — wrote on Twitter today. "I don't think 3+ years is warranted for Weev, but in totality of circumstances, it's understandable."

Still, this is significant time for essentially not hurting anyone, as the British journalist Laurie Penny pointed out. By comparison, the Steubenville rapists were sentenced to just one year in juvenile jail.

This isn't over. Auernheimer is appealing his conviction. And either another example will be made to hackers everywhere, or the sentence will be reduced.

At the end of the day, Weev and co. were nicer to AT&T than, say, hacker HD Moore — who published unpatched iPhone flaws and exposed another big bug in Apple's WiFiwas to Apple. But that doesn't seem to matter much in the boardrooms and courtrooms of America. In their view, all hackers are criminals.

Even many mainstream journalists think all hacking is a crime. Last night on 60 Minutes, for instance, Lara Logan basically accused Jack Dorsey's early work of bordering on just that. And even with the best of intentions, hackers' attempts to route around the system will likely never gain the benefit of the doubt with the public.

Instead, they'll just keep earning jail sentences, at least unless and until the courts — or Congress, though don't hold your breath — push back against prosecutorial overreach. And that, at least, will give them plenty of time to repent at leisure.

Lead image via Flickr user shane_curcuru, CC 2.0; image of Andrew Auernheimer via Wikimedia Commons

Tags:

Oh, The Irony: National Vulnerablity Database Taken Down By Malware

Oh, The Irony: National Vulnerablity Database Taken Down By Malware

As if we needed more evidence that the hackers are winning, here is this: the National Vulnerability Database hosted by the National Institute of Standards and Technology has been stricken with malware and taken offline.

The NVD is a comprehensive database that integrates all of the United State’s government publicly available vulnerability resources. It is a resource to many security firms and security officers at enterprises for tracking day-to-day exploits that malicious hackers could use to breach secure systems.

In an email to security researcher Kim Halavakoski of Finland, NIST said that it had found multiple instances of malware on its public facing NVD websites and took the appropriate action to take the websites offline. 

“The National Vulnerability Database public-facing Web site and several other NIST-hosted Web sites are currently unavailable due to discovery of malware on two NIST Web servers,” wrote Gail Porter from the NIST Public Inquiries Office, according to a Google+ post by Halavakoski as reported by The Register.

Visits to the NVD website confirm that it is indeed unavailable as of 9:00 a.m. EST, March 14. 

The email from Porter to Halavokoski states that NIST’s firewall detected suspicious activity on Friday, March 8 and took steps to block the traffic from reaching the Internet. The malware on the NIST servers was traced to a software vulnerability. NIST said that there was no evidence its websites or the NVD contained or delivered any malware to users. 

“NIST continually works to maintain the integrity of its IT infrastructure and acts to limit the impact of malware on its systems. We regret the impact this has had on our services,” Porter wrote.

Nowadays, everything is a target. That goes for the public facing websites and servers of prominent government agencies such as the NIST and CIA. When it comes to the backbone of government systems (non-public facing servers), those are much harder to crack. That is why we see more distributed denial of service (DDoS) attacks on prominent websites than actual breaches. Much of this DDoS activity came from groups like Anonymous and LulzSec, but the global black hat hacker community has been stepping up its efforts in past years to actually breach internal servers. We have seen this through more advanced spear phishing techniques and the alleged hacker wing of the People’s Liberation Army of China. 

The NIST NVD site makes for an easy target. It is relied upon by many different groups and has a necessary public-facing websites that is, by basic Internet Protocol, vulnerable. NIST played the breach by the book and took the site down. 

Tags:

Thursday, August 23, 2012

Tracking Big Foot: Why GPS Location Requires a Warrant | Center for Democracy & Technology

In a case that raises as many questions as the average sighting of Big Foot, a panel of the Sixth Circuit Court of Appeals ruled earlier this week that law enforcement officers didn't need a warrant to obtain GPS location information generated by his cell phone.

The court’s analysis has been roundly criticized as legally incorrect, lazy, shallow, and vague. I’d like to focus on one aspect of the case that the court missed:  the Department of Justice recommends that police obtain warrants in the scenario presented by this case, does so for good reason, and there were sufficient facts for the government to obtain the warrant that the Department of Justice recommends investigators obtain.

In this case, U.S. v. Skinner law enforcement officers obtained an order that allowed them to monitor for 60 days the location of a pre-paid cell phone they had good cause to believe was being used by Big Foot, the nickname given trucker eventually identified as Melvin Skinner, who they alleged was transporting marijuana.  They obtained a court order under which the provider, Sprint/Nextel, acting at the behest of law enforcement, pinged the phone repeatedly so it would reveal its location over a three-day period and eventually activated the phone’s GPS functionality to locate the phone’s GPS coordinates.   (Sprint/Nextel recently developed a web portal through which law enforcement can do this automatically for the duration of the court authorization, without contacting the provider each time officers ping the phone.)

The court found that there was "… no Fourth Amendment violation because Skinner did not have a reasonable expectation of privacy in the data given off by his voluntarily procured … cell phone."  But, as Jennifer Grannick points out cell phones don’t normally "give off" the kind of GPS location data that law enforcement used to locate Skinner.  Unless the user is employing location services – and Skinner wasn’t – the GPS location data has to be created.  In this case, the provider, under court order, remotely activated the GPS function of Skinner's phone so the police could track him.

There's a critical difference between GPS location information and cell tower location information a mobile phone creates during normal use.  The GPS data in this case is created at the request of law enforcement for tracking purposes and not through the normal use of the mobile phone. The GPS data doesn’t even exist until the provider prompts the device to deliver its GPS location to the provider so law enforcement can access it.  In contrast, providers maintain cell tower location information for business reasons.  Because providers do not normally maintain GPS location information and because it was not voluntarily conveyed to the provider, it is not a "business record" and does not fit into the third party records doctrine, which says that a person has no Fourth Amendment interest in information that is voluntarily revealed to, and held by, a third party.  While the third party doctrine should probably be re-examined, for now we have to live with it, but not for GPS data created by providers at the behest of law enforcement.  For that data, we retain our Fourth Amendment rights against warrantless GPS tracking.  

Blind Eye to Justice

Apparently recognizing that GPS is different, the Justice Department recommends that prosecutors obtain a warrant to get GPS location information from mobile communications service providers.  For example, in this power point presentation the Associate Director of the Justice Department Office of Enforcement Operations recommends that prosecutors use search warrants to get prospective GPS location information (referred to as “lat/long data” or latitudinal and longitudinal data) for constitutional, not statutory reasons, and because "anything less presents significant risks of suppression."  In addition, the Justice Department Associate Deputy Attorney General, testified in April last year that when the government seeks to compel disclosure of prospective GPS coordinates generated by cell phones, it relies on a warrant.

The Sixth Circuit missed this point entirely.  It blithely rejected Skinner's Fourth Amendment claims and implicitly bought into the government's argument that orders under the Stored Communications Act provision at 18 USC 2703(d) can be used to obtain prospective location information that has never been stored.  It did not consider whether the information sought was within the third party records doctrine and it cited no statutory authority for the proposition that the government can compel a provider to create the GPS information for the government to seize.  

Perhaps most ironically, it seems pretty clear that the government had facts establishing probable cause and could have obtained a warrant if it had applied for one.  As the concurring opinion in Skinner noted, law enforcement officials were watching the drug operation for months, had recorded conversations about an upcoming drug run, learned that the courier was carrying a particular phone that they could track, and that a half ton of marijuana was in transit.  

A warrant requirement for location information, as advocated by the Digital Due Process coalition, would still mean a drug courier like Skinner would get caught.  If followed, a statutory warrant requirement decreases the chances a criminal would elude jail because the seized evidence would not be at risk of suppression, as it is now for Big Foot if he appeals this decision. 

For updates, follow us on Twitter at @CenDemTech.

Related Posts

Defending networks from malicious hacking exploits depends in large part on the voluntary, cooperative efforts of network operators, device makers, and Internet users.Today the Broadband Internet Technical Advisory Group (BITAG) -- a group of technical experts dedicated to building consensus about broadband network management -- has released a series of targeted, balanced recommendations to help stifle an emerging type of network attack. That attack has been used in recent years by the hacker...
[Editors Note: This is one in a of series of blog posts from CDT on the Cybersecurity Act, S. 3414, a bill co-sponsored by Senators Lieberman and Collins that is slated to be considered on the Senate floor soon.]Two amendments to the Senate cybersecurity bill now being debated would require government agents to get a warrant before reading a person's email or secretly tracking someone through their mobile phone.  The amendments, if adopted, would be a huge privacy gain and address a long-...
In a new book, CDT experts debate some of the most pressing issues in surveillance law today.Patriot Debates: Contemporary Issues in National Security Law features CDT’s Greg Nojeim in a debate on the third-party records doctrine and its application to criminal investigations in the digital age. The doctrine holds that law enforcement does not need a warrant to search and seize information lawfully held by third parties, such as online file hosting services like Dropbox or online email...
[Editors Note: This is one in a of series of blog posts from CDT on the Cybersecurity Act, S. 3414, a bill co-sponsored by Senators Lieberman and Collins that is slated to be considered on the Senate floor soon.]   Congress is about to decide whether it is a crime to violate terms of service governing your use of Gmail, Facebook, Hulu, or any other on-line service. One of the amendments to the Cybersecurity Act that the Senate is likely to take up this week would substantially increase...

https://www.cdt.org/blogs/greg-nojeim/1708tracking-big-foot-why-gps-location-...

Oversight of Government Privacy, Security Rules for Health Data Questioned | Center for Democracy & Technology

Oversight and accountability for following federal privacy and security rules is critical if the public is going to trust that the next generation of electronic health care providers, insurers, and billing services can protect the privacy of their medical information.  A recent report by the Government Accountability Office questions whether sufficient work is being done to build that public trust.

The GAO report says the Department of Health and Human Services has failed to issue new rules for protecting personal health information and lacks a long-term plan for ensuring that those new rules are being followed.  The HHS Office for Civil Rights (OCR), which is responsible for overseeing these efforts, acknowledged these concerns but noted that rules are winding their way through government channels and that they have "taken the necessary first steps towards establishing a sustainable" oversight program.   

The report's two main concerns are: (1) the urgent need for guidance on de-identification methods, and (2) lack of a long-term plan for auditing covered entities and business associates for compliance with federal privacy and security rules (specifically, HIPAA and HITECH).

De-Identification Guidance

De-identification is a tool that enables health data to be used for a broad range of purposes while minimizing the risks to individual privacy.  Under HIPAA, there are two methods that can be used to de-identify health data. The first is the safe harbor method, which merely requires the removal of 18 specific categories of identifiers, such as name, address, dates of birth or health care services, and other unique identifiers.  The second is the expert determination method that certifies that the data, in the hands of the intended recipient, raises a very small risk of re-identification. The safe harbor method is static and presumes that the removal of the 18 categories of identifiers translates into very low risk of re-identification in all circumstances.

In HITECH, Congress directed HHS to complete a study of the HIPAA de-identification standard by February 2010.  Though covered entities rely more on the safe harbor method because it is easier to understand and more accessible, OCR aimed to produce guidance that would "clarify guidelines for conducting the expert determination method of de-identification to reduce entities reliance on the Safe Harbor method," according to the report.  Two years later and notwithstanding its good intentions, OCR has not released this guidance.  

CDT has met with industry and consumer stakeholders about how to improve federal policy regarding de-identified health data since 2009. CDT also recently published an article in JAMIA proposing a number of policies to strengthen HIPAA de-identification standards and ensure accountability for unauthorized re-identification.  

The OCR should issue the required guidance on de-identification without further delay and continue seeking public feedback on how to build trust in uses of de-identified data.  Foot dragging on this issue risks impeding progress on the ability to monitor the public's health in ways that go far beyond mere notification and routine reporting of symptoms, diagnoses, etc.  With these new capabilities in place, public health officials can move beyond traditional detection and response to outbreaks, enabling earlier disease detection, allowing public health officials to take a more active role monitoring health issues from cancer screening to adult immunizations to HIV.

Ensuring Compliance

Routine audits help ensure that covered entities and business associates comply with HIPAA and HITECH regulations.  Audits also provide OCR with important information about how entities covered by HIPAA and HITECH are implementing critically important privacy and security protections, and potentially surface issues needing further regulatory guidance and helping OCR better determine when penalties for noncompliance are warranted.  

HITECH directed HHS to audit entities covered by HIPAA for compliance with HIPAA and new HITECH requirements; OCR officials began those audits earlier this year. The report states that OCR has no plan to sustain these audits beyond 2012; the report also notes that HHS does not have a defined plan for including HIPAA business associates in its audits. HHS responded that OCR plans to review the pilot audit program at the end of this year and move forward with an audit program after that step is complete.

If the public is to trust that the privacy of their health information is well protected, it must know where that information is going and how it's being used. The report highlights the importance of audits as an effective mechanism for accountability. CDT is encouraged by the progress OCR has made to date in its pilot audit program, and we are pleased to see HHS commit to learning from the pilots to developing and implementing a sustained plan for auditing compliance with federal privacy and security regulations. 

For updates, follow us on Twitter at @CenDemTech.

https://www.cdt.org/blogs/suchismita-pahi/1607oversight-government-privacy-se...